Purdue University lawsuit says Google copied smartphone technology

Purdue University lawsuit says Google copied smartphone technology

The Google brand is pictured at the entrance to the Google workplaces in London, Britain January 18, 2019. REUTERS/Hannah McKay

Register now for Absolutely free unrestricted entry to Reuters.com

Sign up

  • University’s patent covers tech for repairing computer software code
  • Criticism suggests Google engineer copied code for Android software program

(Reuters) – Purdue University’s Purdue Investigate Basis has sued Google LLC in Texas federal court docket, alleging that Android program for eradicating programming problems in smartphones copies areas of its professors’ creation.

The basis requested the U.S. District Courtroom for the Western District of Texas for royalties and an undisclosed sum of revenue damages on Tuesday dependent on Google’s alleged willful patent infringement.

The grievance mentioned two professors and two pupils at the West Lafayette, Indiana university invented the patented technological know-how, which detects software program programming glitches that could have an impact on a mobile device’s electric power management.

Sign up now for Free unlimited obtain to Reuters.com

Register

Purdue stated that right after a Google engineer posted an write-up about a person of the professors in an Android forum in 2012, yet another Google engineer discovered and integrated code disclosed by the inventors into Android software.

Purdue gained the patent in 2019. The university stated it despatched Google a detect of infringement past August, but the enterprise carries on to use the patented code.

A Purdue spokesperson stated in a Wednesday statement that the study basis tried to meet with Google for weeks, but the firm refused “reasonable conditions” for a conference.

The spokesperson said Google infringes multiple additional Purdue patents, and the college will amend its grievance to increase them if Google “proceeds to refuse to negotiate a license.”

Google spokesperson José Castañeda stated Wednesday that the company develops its products independently, and that it was reviewing the criticism and would “vigorously” defend by itself.

The scenario is Purdue Study Foundation v. Google LLC, U.S. District Courtroom for the Western District of Texas, No. 6:22-cv-00119.

For Purdue: Michael Shore and Alfonso Chan of Shore Chan, Mark Siegmund of Steckler Wayne Cochran Cherry

For Google: n/a

Sign-up now for No cost limitless entry to Reuters.com

Sign up

Our Standards: The Thomson Reuters Believe in Concepts.
Read More

Emergency Google Chrome update fixes zero-days used in attacks

Emergency Google Chrome update fixes zero-days used in attacks

Emergency Google Chrome update fixes zero-days used in attacks

Google has released Chrome 95.0.4638.69 for Windows, Mac, and Linux to fix two zero-day vulnerabilities that attackers have actively exploited.

“Google is aware that exploits for CVE-2021-38000 and CVE-2021-38003 exist in the wild,” Google disclosed in the list of security fixes in today’s Google Chrome release.

While Google states that the new version may take some time to reach everyone, the update has already started rolling out Chrome 95.0.4638.69 to users worldwide in the Stable Desktop channel. 

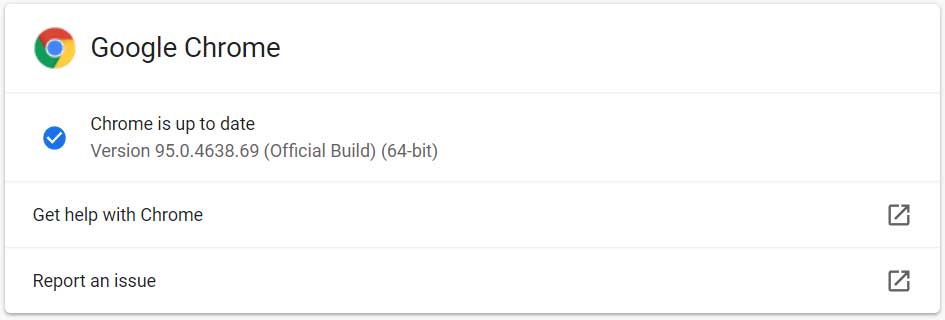
To install the Chrome update immediately, go to Chrome menu Help About Google Chrome, and the browser will begin performing the update.

Chrome 95.0.4638.69 was installed immediately

Google Chrome will also check for available updates and install them the next time you launch the web browser.

Zero-day attacks’ details not disclosed

This Chrome release fixes a total of seven vulnerabilities, with two being zero-days that are known to have been exploited in the wild.

The first zero-day, tracked as CVE-2021-38000, is described as an “Insufficient validation of untrusted input in Intents” and was assigned a High severity level. This vulnerability was discovered by Clement Lecigne, Neel Mehta, and Maddie Stone of Google Threat Analysis Group on September 15th, 2021.

The second zero-day, tracked as CVE-2021-38003, is a High severity “Inappropriate implementation” bug in the Chrome V8 JavaScript engine. This vulnerability was discovered by Lecigne as well and reported on October 24th.

At this time, Google or the researchers have not provided further details regarding how threat actors used the vulnerabilities in attacks. However, as Google discovered the vulnerabilities, we may learn more in future reports by Google TAG or Project Zero.

As these two vulnerabilities have been used in attacks, it is suggested that all Chrome users perform a manual upgrade or restart their browser to install the latest version.

Fifteenth zero-day fixed this year

With these fixes, Google has patched 15 Chrome zero-day vulnerabilities since the beginning of 2021.

The other thirteen zero-days patched this year are listed below:

  • CVE-2021-21148 – February 4th, 2021
  • CVE-2021-21166 – March 2nd, 2021
  • CVE-2021-21193 – March 12th, 2021
  • CVE-2021-21220 – April 13th, 2021
  • CVE-2021-21224 – April 20th, 2021
  • CVE-2021-30551 – June 9th, 2021
  • CVE-2021-30554 – June 17th, 2021
  • CVE-2021-30563 – July 15th, 2021
  • CVE-2021-30632 and CVE-2021-30633 – September 13th
  • CVE-2021-37973 – September 24th, 2021
  • CVE-2021-37976 and CVE-2021-37975 – September 30th, 2021

As Google is now pushing out Chrome updates to fix zero-days as they are reported, it is strongly advised that users do not block updates and install new versions as they become available.

https://www.bleepingcomputer.com/news/google/emergency-google-chrome-update-fixes-zero-days-used-in-attacks/…

Read More